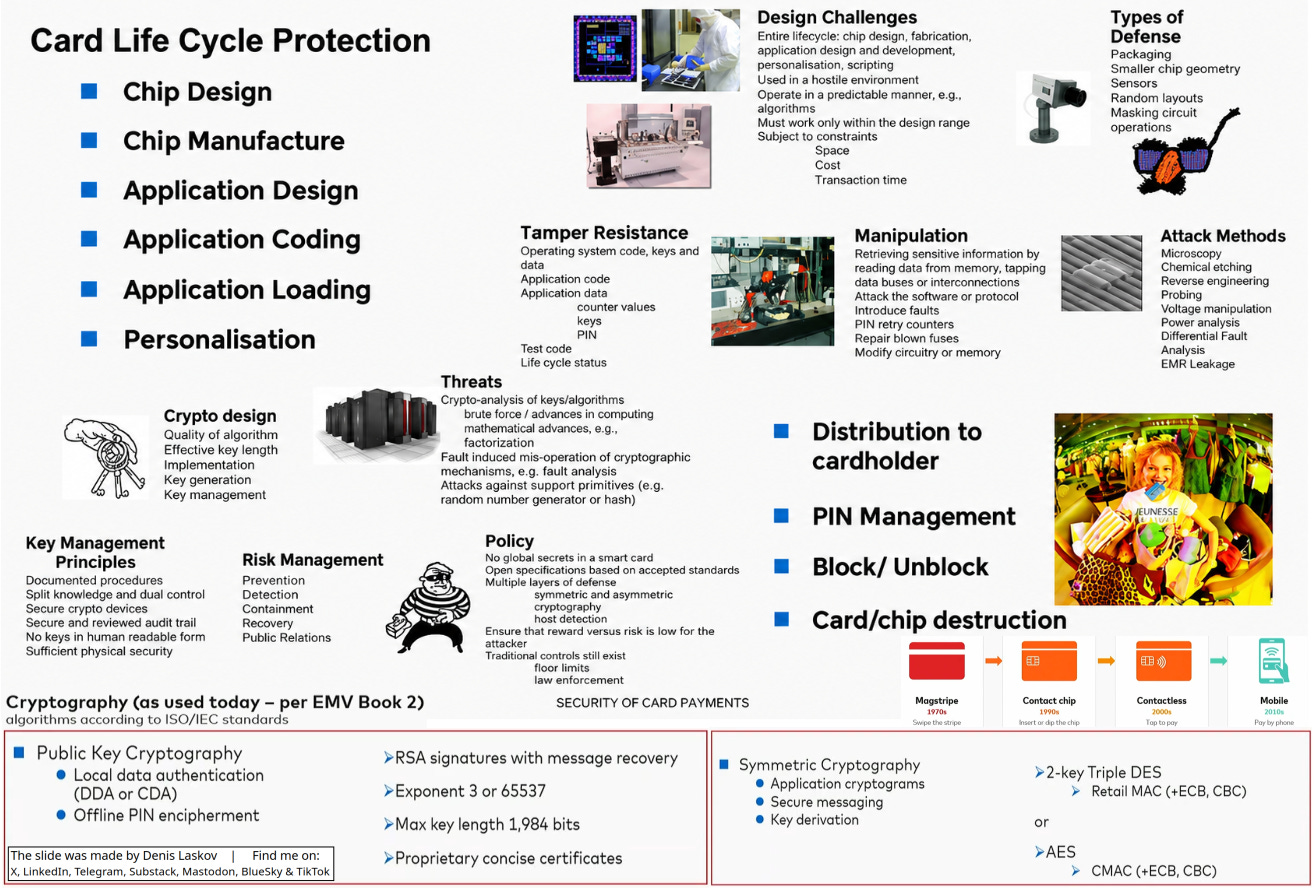
Security and payments expert Michael Ward gave a public lecture a couple of months ago about security in face-to-face card payments, especially the protocols between the card, terminal, and issuing bank.
This is the basics of fintech cybersecurity and a must-know for everyone who deals with credit card fraud, skimmers, and how to defeat them. It is also a great source of knowledge about why specific tech was chosen.
Interesting insight: Mastercard uses one 1984-bit public key installed in every terminal worldwide. Why not 2048-bit or 4096-bit? Because EMV keys are (or were) restricted to less than 1984 bits, so Mastercard decided to use the maximum allowed.
And it will last until at least 2035. :)
Definitely recommended to anyone who is interested in credit card security, payment systems, and how to hack them. Enjoy!
More details:
Security for Payments [Youtube]: https://lnkd.in/dbFPNWUy